
B2B Healthcare Email Compliance: CAN-SPAM rather than HIPAA
Sending sales emails to healthcare providers at their practice addresses is a CAN-SPAM question rather than a HIPAA question. Here is what the law requires. Source: FTC CAN-SPAM guide.
Updated April 2026
The Most Common Misconception in Healthcare Sales
Healthcare teams sometimes treat every communication involving a physician as a HIPAA issue. That collapses two separate questions: whether a message contains protected health information and whether a commercial email satisfies CAN-SPAM. The FTC states that CAN-SPAM covers commercial messages and makes no exception for business-to-business email. Source: FTC CAN-SPAM guide.
HIPAA governs protected health information (PHI). The HIPAA Privacy Rule restricts how covered entities (healthcare providers, health plans, and healthcare clearinghouses) and their business associates handle individually identifiable health information. It has nothing to do with a medical device company emailing a surgeon about a new implant system. It has nothing to do with a health IT vendor emailing a practice administrator about EHR integration. Those are B2B commercial communications, and they're governed by the same laws that govern any other B2B email: primarily the CAN-SPAM Act.
Where the confusion comes from. Healthcare organizations spend enormous effort on HIPAA compliance. Every employee takes annual HIPAA training. Every vendor signs a Business Associate Agreement. HIPAA is so pervasive in healthcare culture that people assume it governs all communications involving healthcare professionals. It doesn't. HIPAA applies to PHI, patient names, diagnoses, treatment records, billing information. A physician's business email address and practice phone number are not PHI. These are professional contact information, publicly available through the NPI registry and other directories.
The practical advantage is a documented review process. A healthcare vendor can classify the message, identify the data used, apply CAN-SPAM's commercial-email requirements, check applicable privacy and product-promotion rules, and retain evidence of the decision. That approach supports legitimate outreach without treating HIPAA as a blanket answer to every business communication. Sources: HHS covered entities and business associates and FTC CAN-SPAM guide.
This guide explains the federal commercial-email baseline and the separate issues a healthcare seller should review. It is a factual overview, not legal advice. Consult qualified counsel about the laws and facts that apply to a specific campaign. Sources: HHS covered entities and business associates and FTC CAN-SPAM guide.
CAN-SPAM Requirements for B2B Healthcare Emails
The CAN-SPAM Act of 2003 is the primary federal law governing commercial email in the United States. It applies to any "commercial electronic mail message", defined as email whose primary purpose is the commercial advertisement or promotion of a commercial product or service. A sales email to a physician or practice administrator falls squarely within this definition. Source: FTC CAN-SPAM guide.
CAN-SPAM does not require prior opt-in for B2B emails. This is a critical point. Under U.S. federal CAN-SPAM rules, a commercial email may be sent without prior consent if the sender follows the law's identification, disclosure, opt-out, and other requirements. Other jurisdictions use different consent and data-processing rules, so this U.S. baseline should not be applied to international recipients. Source: FTC CAN-SPAM guide.
The seven CAN-SPAM requirements. Every commercial email you send must comply with these rules, per the FTC's compliance guide:
1. No false or misleading header information. Your "From," "To," and "Reply-To" fields need to accurately identify the person or business sending the message. You can't spoof a hospital's domain or pretend to be a colleague of the recipient. Source: FTC CAN-SPAM guide.
2. No deceptive subject lines. The subject line must accurately reflect the content of the email. "Urgent patient referral" as a subject line for a sales email is deceptive. "New data integration for [their EHR]" is fine if the email discusses that. Source: FTC CAN-SPAM guide.
3. Identify the message as an advertisement. The law requires disclosure that the message is an ad. The FTC gives flexibility in how you do this, it doesn't need to be a large banner. A footer line such as "This is a commercial message from [Company]" is generally sufficient. Source: FTC CAN-SPAM guide.
4. Include your physical postal address. Every commercial email needs to contain the sender's valid physical postal address. A street address, a P.O. Box registered with the U.S. Postal Service, or a private mailbox registered with a commercial mail receiving agency all qualify. Source: FTC CAN-SPAM guide.
5. Provide a clear opt-out mechanism. Every email must include a clear, conspicuous way for the recipient to opt out of future emails. This can be an unsubscribe link or a reply-to address with opt-out instructions. Source: FTC CAN-SPAM guide.
6. Honor opt-out requests within 10 business days. Once someone opts out, you must stop emailing them within 10 business days. You cannot charge a fee, require information beyond an email address, or make the recipient take multiple steps to unsubscribe. Source: FTC CAN-SPAM guide.
7. Monitor what others do on your behalf. If you hire a third party to send emails for you, you're still legally responsible for compliance. This includes outsourced SDR teams, marketing agencies, and email service providers. Source: FTC CAN-SPAM guide.
HIPAA applies to covered entities and business associates. Covered entities include health plans, healthcare clearinghouses, and healthcare providers that transmit health information electronically in covered transactions. A business associate performs certain functions or services for a covered entity that involve protected health information. HHS states that an entity outside those definitions does not have to comply with the HIPAA Rules. Source: HHS covered entities and business associates.
Even if your company is a business associate of some healthcare clients, that relationship doesn't extend to your sales emails. A Business Associate Agreement (BAA) governs how you handle the PHI that specific client shares with you. It doesn't restrict you from emailing other physicians about your product. Those are completely separate activities.
The content and context of the information matter. HHS defines protected health information as individually identifiable health information held or transmitted by a covered entity or business associate. A campaign team should stop and obtain privacy review if a proposed message or targeting field uses information about an identifiable patient's condition, treatment, or payment. Source: HHS Privacy Rule summary.
Provider directory fields and patient records are different data contexts. The CMS NPI Registry publishes provider identity and submitted practice information. A business email may come from another public or commercial business source. Neither fact, by itself, decides every privacy question; teams should record the source, permitted use, and applicable law for each campaign field. Source: CMS NPPES files.
Keep operational care communications separate from sales outreach. A message that uses identifiable patient information belongs in the covered entity's or business associate's HIPAA-governed workflow. A commercial product message must be assessed under CAN-SPAM and any other applicable law. Do not reuse patient data to create a sales audience. Sources: HHS Privacy Rule summary and FTC CAN-SPAM guide.
State-Specific Laws and Additional Considerations
CAN-SPAM supplies a federal commercial-email baseline. State privacy laws can separately govern how a company collects, uses, sells, or shares personal information. Determine which laws apply to the business, recipient, data source, and processing activity instead of assuming the federal email rule answers every privacy question. Sources: FTC CAN-SPAM guide and California Attorney General CCPA guidance.
California (CCPA, as amended). The California Attorney General's CCPA guidance describes consumer rights and covered-business obligations. It also states that the former exemption for personal information reflecting business-to-business transactions expired on December 31, 2022. A campaign using California business-contact data should be reviewed against the current statute, regulations, and the company's data practices.
Other state laws. Applicability and exemptions vary by jurisdiction and can change. Maintain a jurisdiction-specific inventory with counsel, record the rule applied to each audience, and update suppression and privacy-request workflows when requirements change.
Industry-specific considerations. Regulated product promotion can add another review layer. The FDA's Office of Prescription Drug Promotion oversees prescription-drug promotional communications to healthcare professionals and consumers. Teams marketing drugs or devices should have the appropriate regulatory reviewer assess product claims in addition to the commercial-email workflow. Source: FDA prescription drug advertising and promotional labeling.
Professional courtesy norms. Practices and health systems can set their own vendor-communication preferences and routing policies. Record and honor those preferences in the suppression process even when they are stricter than the legal baseline.
International recipients. Canada's CASL generally requires consent for commercial electronic messages and recognizes express consent and specified forms of implied consent. In the EU, the GDPR requires a lawful basis for processing personal data; legitimate interests may apply to direct marketing only after a documented assessment, and email use must also comply with applicable ePrivacy and member-state rules. Review jurisdiction-specific requirements with counsel before sending. Sources: CRTC CASL guidance; European Commission legal grounds for processing.
Email List Hygiene and Data Quality
Compliance isn't just about following rules in the emails you send. It also depends on applying those rules consistently to the audience and records used for each campaign.
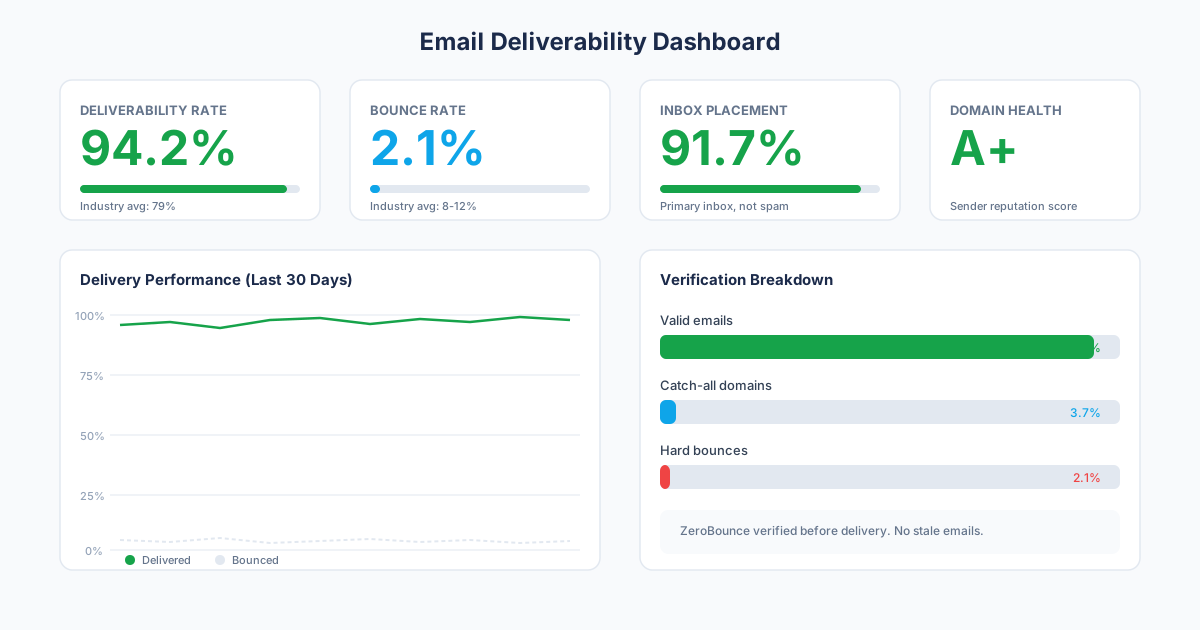
Bounce management. Invalid addresses create delivery failures and waste outreach. Remove confirmed hard bounces, define a documented policy for repeated soft bounces, and use the requirements published by your sending platform when setting operational thresholds.
Opt-out list maintenance. Every company sending commercial email must maintain a suppression list of everyone who has opted out. This list must be checked against every outbound email campaign. Sounds obvious; however, in practice, it breaks down when companies use multiple email tools, when reps send from personal email clients, or when contact lists get shared across teams without syncing the suppression list. Centralize your suppression list and make it the single source of truth. Source: FTC CAN-SPAM guide.
Data freshness. Healthcare contact data changes continuously as physicians retire, change practices, or join new systems and as practices rebrand or are acquired. Record the source and verification date for each address, monitor your own bounce and change rates, and set a refresh cadence from that evidence rather than relying on a generic industry percentage.
Source verification. Know where each email address came from and retain that provenance. Treat public registries, professional directories, commercial datasets, practice websites, and user-submitted records as distinct sources with different coverage and verification needs. Review the collection method and applicable law before using an address for outreach.
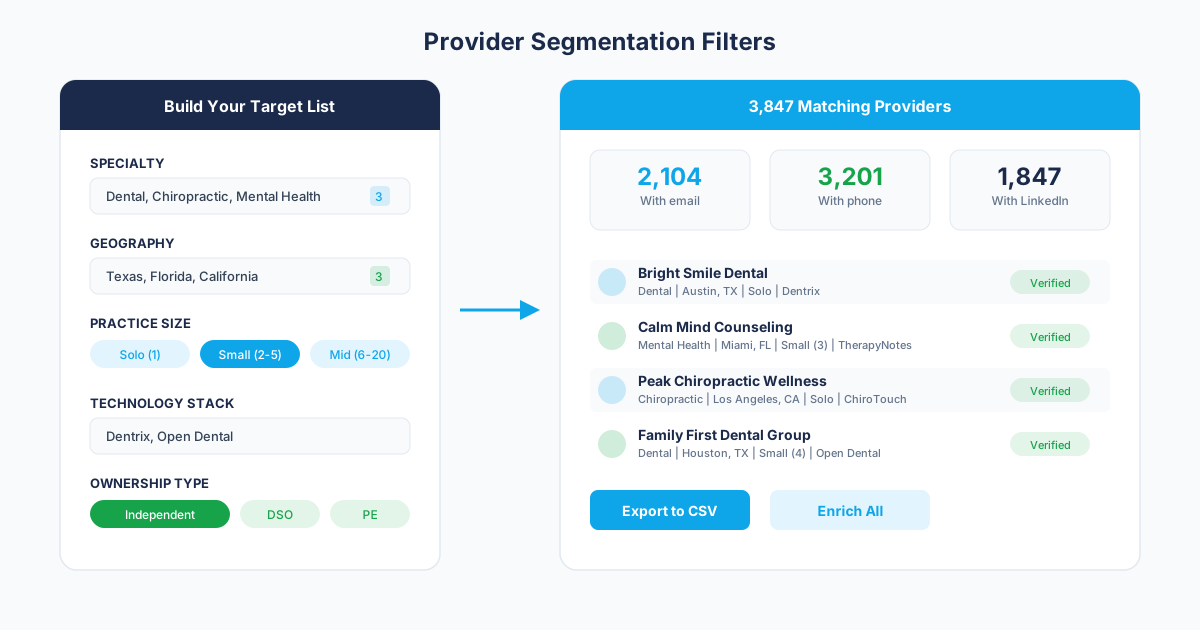
Segment before sending. Use specialty, practice type, geography, and product relevance to avoid obviously irrelevant outreach. Measure each segment's delivery, reply, conversion, complaint, and opt-out results separately; do not assume a universal performance lift.
Document your compliance processes. Maintain an internal record of how you collect email addresses, manage opt-outs, verify data sources, and review campaign content. Keep the process concise enough that the team can apply it consistently and update it when tools, jurisdictions, or sending practices change.
Frequently Asked Questions
Can I send a cold email to a physician at their practice email address?
The FTC states that CAN-SPAM covers commercial messages and makes no exception for business-to-business email. Its guide lists the federal rules for those messages. Separately assess the message content, data source, and other applicable requirements. Source: FTC CAN-SPAM guide.
Does HIPAA apply to B2B healthcare marketing emails?
HIPAA applicability depends on whether the sender is a covered entity or business associate and whether the activity involves protected health information. HHS states that an entity outside those definitions does not have to comply with the HIPAA Rules. Source: HHS covered entities and business associates.
What happens if I violate CAN-SPAM when emailing healthcare providers?
The FTC's current compliance guide states that each separate email in violation can be subject to a penalty of up to $53,088. It also describes aggravated violations that can trigger additional fines or criminal penalties. Review the current FTC guidance and get legal advice for a specific campaign. Source: FTC CAN-SPAM guide. Source: https://www.ftc.gov/business-guidance/resources/can-spam-act-compliance-guide-business.
Do I need a Business Associate Agreement (BAA) to email physicians about my product?
A BAA is tied to a covered entity engaging a business associate for functions or services that involve protected health information. Determine whether that relationship and data use exist instead of deciding from the recipient's profession alone. Source: HHS covered entities and business associates.
What evidence should a campaign compliance file retain?
Keep the source of each business address, the collection date, sender identity, message version, suppression check, unsubscribe event, and the policy applied. Counsel can then review the actual workflow rather than a summary.
Related Resources
Get the Provider Data You Need
Tell us what you're looking for. We'll build a custom list matched to your target market.
Trusted by healthcare sales teams, medical device companies, and health IT vendors across the US.